IMPORTANT NOTIFICATION

This site is an archive of Simon's first blog.
Current writing and commentary is now published at
simonedwards.com.
Showing posts with label rootkit. Show all posts

Tuesday, 25 November 2014

Regin: When did protection start?

Regin, advanced malware that is most likely a government espionage tool, is making headlines.

This is because it's a very well-constructed set of tools and also because observers are surprised at how successful it was. It also targeted GSM networks, which is novel.

The big question is, how could the major anti-malware firms have missed this threat for so long?

Or, one might ask, did they really miss it or quietly detect it?

Some people appear to believe that, as Regin was probably created and used by Western governments, then Western anti-malware companies colluded to ignore the threat.

Symantec seems to have been slow to notice Regin because its write-up of Backdoor.Regin claims that it was discovered in December 2013, which is much later than March 2011, when Microsoft updated its definitions to include Regin.A.

In an effort to find a history of Symantec's detection of this malware I obtained an archive of Regin samples from security researcher Claudio Guarnieri and asked the kind folk at VirusTotal to discover when, if ever, Symantec's scanner first detected each sample.

Before we look at these results I want to be clear about what these results mean and what they do not because VirusTotal data is easily abused and dodgy conclusions readily-reached.

The table below indicates that Symantec's technology was capable of detecting most of the samples as being at least suspicious from February 2010. It then made a clearer classification of being a 'Trojan' from March 2011.

Only yesterday (24th November 2014) did it officially label the threat as 'Regin'. This corresponded to its announcement of the Regin threat.

Usually the problem with using VirusTotal is that someone will upload some files, show that product X failed to recognise them and then conclude that the product, or the entire anti-virus industry, is useless.

In this case we can see dates relating to when the product detected the files as threats. Possibly the product would have protected against these files even earlier, and possibly those that appear as having been missed (Classification = 'nothing') would have been stopped through some other layer of protection not related to file signatures.

So I see the following as a worst-case scenario. Symantec's scanner recognised most of these files as threats from around 2011 onwards. Maybe it was capable of stopping them and maybe not - we can't know that for sure. But it's fair to assume that if a signature-based scanner can recognise a file then it will probably generate an alert at the very least.


I've focussed one Symantec simply because it first announced the Regin malware, minutes before other vendors joined in.

Friday, 26 April 2013

Introduction to malware forensics

Earlier this month I was delighted to sit on a discussion panel at Kaspersky Lab's reviewers workshop in Lisbon.

I later demonstrated some tools and techniques for analysing the behaviour of malware. I have provided links to the tools and some other useful resources.

(left to right) Peter Stelzhammer, Sveta Miladinov, Simon Edwards and Andreas Marx
The area that I focussed on involved detecting rootkit-related malware in tests. Usually you can't tell if there are hidden processes running using conventional tools.

At Dennis Technology Labs we always check for hidden processes using some advanced techniques usually reserved for malware analysts and forensics investigators.

To get a short insight into how we do that (and how you can), take a look at the link above.

Following a series of interviews, Arne Arnold from PC-Welt wrote an interesting article that shows the difference in opinions of testers and analysts. [Original (German); a poor Google Translation (English)]

Monday, 15 April 2013

Is it infected?

How do you know if a system is infected with malware?

This question is important to journalists, testers and other reviewers of anti-malware software.

The security product may claim to have defeated the threat but you need to dig down into the system using forensic tools to be sure that it has succeeded.

The following links and notes are intended for the journalists who attended Kaspersky Lab's reviewers workshop this week:

Wireshark
http://www.wireshark.org/download.html
http://wiresharkdownloads.riverbed.com/wireshark/win32/Wireshark-win32-1.8.6.exe
http://wiresharkdownloads.riverbed.com/wireshark/win64/Wireshark-win64-1.8.6.exe

CaptureBAT
https://www.honeynet.org/node/315
https://www.honeynet.org/files/CaptureBAT-Setup-2.0.0-5574.exe

>> CaptureBAT.exe -l demo.txt -n -c

Autoruns

http://technet.microsoft.com/en-US/sysinternals


WinPrefetchView
http://www.nirsoft.net/utils/win_prefetch_view.html
http://www.nirsoft.net/utils/winprefetchview.zip

Volatility
https://code.google.com/p/volatility/
https://volatility.googlecode.com/files/volatility-2.2.standalone.exe

>> volatility-2.2.standalone.exe -f stuxnet.raw pslist

>> volatility-2.2.standalone.exe -f stuxnet.raw psscan

>> volatility-2.2.standalone.exe -f stuxnet.raw psxview

Malware Analyst's Handbook
http://www.malwarecookbook.com
http://goo.gl/7gONZ (specific page on Amazon.com)

Stuxnet analysis
http://mnin.blogspot.co.uk/2011/06/examining-stuxnets-footprint-in-memory.html

Thursday, 29 March 2012

Why even experts need antivirus

[This article is written in response to Wired's recent article, Is Antivirus Software a Waste of Money? As is usually the case, when you see a headline posed as a question, the answer is usually "no".]
"I don't run anti-virus, actually," he said, "and I've never had a virus."

"Really?" I asked. "How do you know?"

"I think I'd know," he scoffed.

I had that conversation with the UK head of marketing for an anti-virus company that, while not one of the top brands, is certainly quite well known in Europe. We probably spoke around 2008.

Scroll back to the eighties and possibly even early nineties and he'd probably be at least half right. Viruses might hide for a while but they usually gave away their presence at some stage, possibly by deleting or encrypting files, sending a cheeky message or producing a graphic effect that was hard to ignore.

In the later parts of the nineties things started to change. Malware began to commercialise, and it made sense for these malicious programs to be more subtle. Dialers were one of the first such threats. They resided silently on victims' systems and made phone calls to premium numbers.

Once malware started to hide, the game changed. Without appropriate tools even an expert would not know that a system was infected. Even then, sensible behaviour, such as avoiding pirated software, license key generators and pornography websites was sufficient to avoid most problems.

Halfway through the noughties (around 2005-6) a new approach rendered the classic advice of "be careful" fairly useless.

Criminals started compromising legitimate websites, loading malware from otherwise innocent sites onto visitors' computers. In many cases users would have no idea that this was happening. Even a paranoid expert would have a tough time using the internet in a useful way without exposing their computer to such threats.

Rootkits are also now prevalent. It is hard to detect these threats even with specialised software, let alone some sort of tuned-in, Jedi-like human virus-detector sense.

In Wired's article Is Antivirus Software a Waste of Money? a startup CEO called Dan Guido was quoted as saying, "If it weren’t for [compliance] nobody in the security industry would run [anti-virus]."

I contacted Dan to see if he was happy with the angle of the article. He was, by and large, and claimed that,
"The issue with AV is that their virus detection capabilities only become effective after tens of thousands of people have been compromised with the same virus and days or weeks after that virus was first observed."
Having seen how some anti-malware tackles new attacks, sometimes involving zero day exploits, I don't agree with his blanket statement. He went on to make other very general assumptions about how anti-virus software works. One notable point of view was,
"At the time of infection, every major attack group has procedures that allow it to avoid all the known checks that AV runs through."
In other words, criminals check their malicious software before releasing it, checking to see if anti-virus will catch it. This is certainly true.

Underground versions of VirusTotal-style services exist but I find it hard to believe even the most advanced attacker is capable of running a full end-to-end test to ensure success without alerting the anti-virus vendors.

For example, they must either allow or block cloud service queries. Block these queries and the test is not complete. Allow them and information is fed back about the new threat to the vendor.

I polled a few security professionals, in an admittedly unscientific study, and found that they all used anti-virus. No one believes that anti-virus is a panacea. It's just daft to run without it.

Despite this Lance Spitzner sent me a Twitter message, guessing that maybe experts don't use anti-virus "because most security professionals use a Mac :)" Having been to very many security conferences I have to admit that he has a point.

Thursday, 12 January 2012

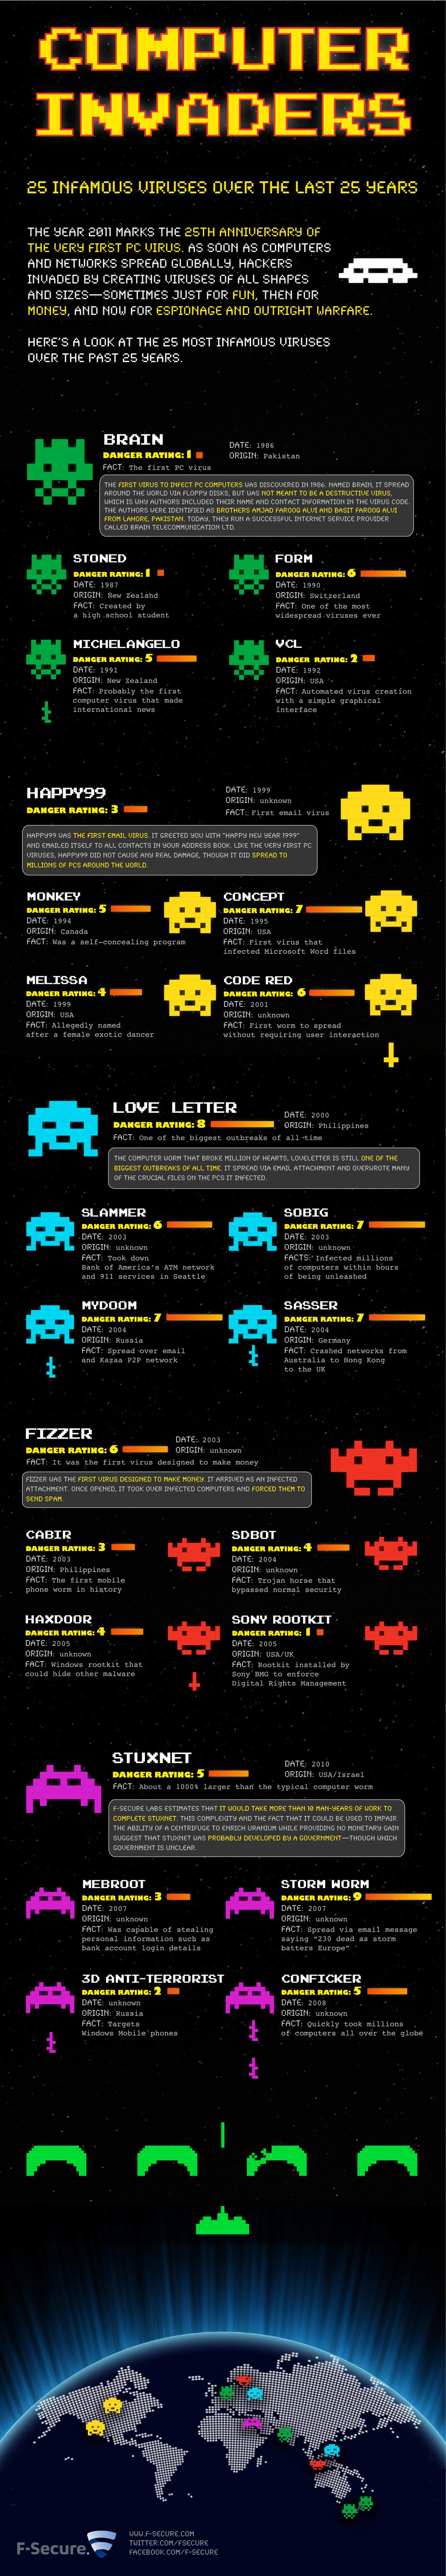
25 years of computer viruses in pictures

F-Secure has produced a graphical summary that shows some of the most talked-about computer viruses.

You can view the entire 'infographic' or download a high-resolution version from F-Secure's blog.

To summarise, quickly, the history starts with Brain; runs through the likes of Melissa, Code Red and Love Letter (aka ILoveYou); and concludes with Stuxnet and Conficker.

Interestingly the chart includes Sony's used of rootkit-like technology. This not a virus, but uses an approach also used by some malware. Additionally, many of the other threats are actually worms rather than viruses.

Wednesday, 30 November 2011

Mobile rootkit update: video

One week ago Trevor Eckhart reported that HTC phones were loaded with secret software designed to monitor pretty much anything on a smartphone. The story of potential wholesale monitoring was disturbing and was made more so by the legal threats made against him at the time for disclosing the issue.

Eckhart has now released video footage showing how the software is hidden and, most interestingly, the level of logging that it provides. Essentially he monitors the monitor and discloses the information that it collects.

This information includes details (including the text of) SMS messages, the handset's location and even records of the specific handsets buttons that are pressed by the user - in real-time. 


Friday, 25 November 2011

Stuxnet explained: video

Stuxnet is one of the most interesting pieces of malicious code found in the last few years.

It provides significant evidence that nation states are using computers to undermine each other.

The well-made video below explains what Stuxnet is (a weapon in code form), what it did and poses some questions about the future.

It suggests, incorrectly as far as I know, that the source code is available. Thus far it is not "open source", as claimed in the video.

This is one of many pieces of recent media that explores the concept of cyber war. It is a controversial area, largely because there is little proof. Stuxnet is tangible evidence, which is why security companies are so excited about it.

Cold war, cyber war or simply war?

Eugene Kaspersky has just written an interesting article that poses the view that this type of cyber war, in which malicious code is used as a form of weapon, is a series of acts of international aggression. He believes that it is tantamount to cyber terrorism.

Malicious code such as Stuxnet can do a few things but one of the most interesting characteristics is its capacity for sabotage. In the Cold War of the 1980s there were claims of sabotage, but rarely anything as direct as the tasks that Stuxnet is capable of carrying out.

One similar incident involved the Trans-Siberian pipeline back in 1982. The US is said to have planted a logic bomb that resulted in a massive explosion. Rather than introducing a virus from a network or USB key, the theory goes that US programmers planted the malicious code into a program that they knew would be stolen by the Russians.


Stuxnet: Anatomy of a Computer Virus from Patrick Clair on Vimeo.

Thursday, 24 November 2011

Computer virus theory on missile explosion

Did a computer virus cause the explosion of an Iranian ballistic missile, capable of carrying a nuclear warhead?

The story that is doing the rounds claims that on the 12th November 2011 a missile exploded in an Iranian army base. A number of Iranian officers and rocket experts were killed.

The Stuxnet worm is considered to be the culprit.

So far the facts seem rather vague, as the coverage of this event stems almost entirely from a report on one website, that being Debkafile. This site appears to be "unabashedly in the hawkish camp of Israeli politics" and uses unattributed sources extensively.

Taking this main report on its merits, let's see what the 'facts' are, versus the 'theory'. I'll assume that the following four details are accurate:

  1. Maj. Gen. Moghaddam presents a new type of warhead to experts.
  2. He runs a computer simulation on a system attached to the missile.
  3. The missile explodes, killing over one dozen people.
  4. The extent of the explosion means that there are no witnesses and little physical evidence.
The Debkafile report also notes the following:
  1. The missile exploded because the computer sent it an order to do so.
  2. Iranian intelligence have two theories:
    • Western or Israeli intelligence services planted a technician, who sent the signal ordering the missile to explode.
      [Note: I think the reporter meant that the technician programmed, rather than signalled, the computer.]
    • The computer was responsible, having been infected with the Stuxnet worm.
  3. Iranian intelligence considers the second theory (above) to be more plausible than the first.

To summarise, a missile has exploded in an apparent accident and there are no living witnesses. The computer involved is completely destroyed, as is the missile.

Somehow Debkafile is able to deduce that the computer sent the order to explode, despite no apparent evidence to support this. This is a significant problem with Debkafile's report. It contains no attributed facts, just statements of fact without any evidence.

Which of the following do you think is more likely?:

  1. The missile exploded, accidentally.
  2. A spy programmed a computer to explode the missile.
  3. A computer virus programmed a computer to explode the missile.

It's coming to something when the idea of computer viruses exploding nuclear-capable missiles is more plausible that accidents or more mundane methods of sabotage.

Wednesday, 23 November 2011

Pre-installed rootkit spies on mobile users

Rootkit software is pre-installed on mobile handsets sold by major network operators.

The software allows a remote administrator to spy on an individual, checking their location, what software they are running on the phone and what keys they are pressing.

This news comes from Trevor Eckhart, who recently brought attention to a logging application that is pre-installed on HTC devices. That program opened up the possibility of an attack against a phone. His latest discovery is potentially more serious and sinister. Possibly that is why he has been threatened with legal action.

In an article posted on Android Security Test, Eckhart notes that:
"Carrier IQ (CIQ) sells rootkit software included on many US handsets sold on Sprint, Verizon and more. Devices supported include android phones, Blackberries, Nokias, Tablet devices and more."
The company says that its solutions have "revolutionized the way mobile operators and device vendors gather and manage information from end users." The question is, what is this information used for? CIQ claims that it's for troubleshooting and other diagnostic purposes.

Eckhart notes that the level of power the software provides to external administrators is high:
"...instead of seeing dropped calls in California, they now know 'Joe Anyone's' location at any given time, what he is running on his device, keys being pressed, applications being used."
This information was reported last week in various places, but today it seems that Eckhart is facing possible legal action over copyright infringement. CIQ apparently did not take kindly to the distribution of some training material, or Eckhart's characterisation of its software as a rootkit.

There seems to be a recent spate of legal threats against security researchers.

Wednesday, 16 November 2011

A guide to rootkits

Eugene Kaspersky, of Kaspersky Lab fame, has published a short article on rootkits.

It's not too technical for most to understand; it links to an interesting test of anti-virus software versus pre-installed rootkits; and it notes the easy availability of rootkits on the black market.

Eugene writes that, "rootkits are not all bad/malicious," but that, "the general public has come to view this technology as a bad thing."

However, he concedes that, "rootkits represent really dangerous technology."

In the past 'legitimate' uses of rootkit methods have been PR disasters. For example, Sony's adventures with rootkits actually made systems more vulnerable to other threats.

Jail breakers open cells via internet

Researchers have found a way to open prison doors remotely from the internet.

The discovery came hot on the heals of a strange event one Christmas eve, when all of the doors to a US prison's death row cells opened, apparently on their own.

An investigation into this potentially disastrous event found that the problem was due to an electrical fault. However, further checks revealed that the door locks could be tripped on purpose. Furthermore, while prison locking systems are not supposed to have any internet connectivity, in practice this seems not to be the case.

Sean McGurk, formerly of the US Department of Homeland Security, claims that when he inspected over 400 prison facilities, "in no case did we ever not find connections. They were always there."

The discovery that prison door locks can be hacked over the internet was made by ex-CIA officer John Strauchs. He claims that maximum security prisons use programmable logic controllers (PLCs) to handle automating door locking and unlocking. PLCs were hacked in the infamous Stuxnet attack on Iranian nuclear facilities.

The Stuxnet worm was able to reprogram the systems controlling centrifuges used to enrich Uranium. It did so in a way that would damage the equipment and, therefore, slow down the Iranian nuclear programme. Strauchs took a similar approach to his research and has demonstrated an internet attack on prison doors. It seems from his description as if he used a rootkit-type approach.

"You could open every cell door, and the system would be telling the control room they are all closed," he told The Washington Times.

In an interview with VentureBeat he also proposed another, possibly more sinister scenario than a mass jailbreak. He imagined the possibilities of an assassination in which, "if you are a [gang member], you prevent a door from opening, and you start a prison fire."

Strauchs presented his findings at the Halted Hacker conference in Miami on 26th October 2011.

Thursday, 27 October 2011

Anti-virus myths busted

Last week I gave the début presentation of my anti-virus myths talk at the London International Technology Show.

A few people have asked for access to the basic information that I used, so here it is. The talk lasted for around 40 minutes so this really is a bare-bones summary.

Myth #1: Anti-virus protects 100%
Real-world protection tests by Dennis Technology Labs (DTL) and other testers show that even well-known brands of security software can be compromised by malware.

Myth #2: Anti-virus slows PCs
In performance tests conducted by DTL, most popular anti-virus software makes virtually no impact on general system performance.
However, system startup (boot) times can be affected, as can shutdown times. These are important because they are very noticeable by users.
Myth #3: I don’t need it (I’ve never been infected)
Current threats tend not to make themselves known to the casual observer. Rootkits make it hard, even for experts. 
Myth #4: Viruses stay in the bad bits of the internet
While some areas of the internet are riskier than others, legitimate sites can be infected. We demonstrated a real, legitimate site infecting our test PC.
Myth #5: Protection costs a lot
Free products are OK, while commercial products often come with multiple licenses.
Myth #6: Avoid Internet Explorer
All popular browsers have security holes. Internet Explorer has fewer known issues than Opera and Firefox. Chrome and Safari are not immune*.
Myth #7: My ISP will save me
There is no business reason why it would, without raising subscription costs. We covered various options to reduce exposure to threats, including ISP-like techniques such as using special DNS services.
Myth #8: Salvation is a Mac, Linux or Android
Attackers go for popular systems. As Mac and Android users become more prevalent so will the threats to those systems. There are more known sets of vulnerabilities for OS X and Linux than there are for Windows*.

The following video clip was taken by one of the audience. Special thanks to PDTalkinTech for providing the photos and this video footage from part of the presentation:


* Data on software vulnerabilities was provided by Secunia.

Wednesday, 5 October 2011

Kaspersky rescue CD

If your system becomes badly compromised by malware then one approach to fixing it is to boot from a read-only disk (such as a CD disc) and run a scanner from a safe, uninfected environment.

Kaspersky provides a free bootable rescue CD that includes an anti-virus scanner. Other vendors do the same, but I mention Kaspersky here because a previous article, about an older version, is one of the most popular posts on this blog and still attracts large numbers of visitors. Hence the belated update.

The disc contains a live Gentoo Linux operating system that can run in text or graphical mode. It is compatible with 32- and 64-bit x86 systems (i.e. normal PCs). As you might hope, you can download updates before running a scan.

Interestingly, if you are scanning a system that already has a Kaspersky anti-virus program installed the updater will check the update files already available and only download those that are not available locally.

A utility called Kaspersky USB Rescue Disk Maker is also available from the site. It takes the contents of the Rescue Disk and copies it to a USB device, which you can then use to boot an infected PC.


More documentation is available from Kaspersky's Technical Support site.

Tuesday, 4 October 2011

Linux may be rooted

Linux developers have been asked to check their systems for signs of rootkits. The warning comes after Linux leaders discovered that important servers had been compromised.

The advice given to developers is to re-install their operating systems. Alternatively the alerting email lists three Linux anti-rootkit tools. Then it's a matter of double-checking the package signatures and other onerous tasks.

The rootkit tools mentioned are:

The email thread includes some useful and interesting tips for securing Linux systems, and handling those that one suspects as being compromised.

ISP warns of 'virus' infection

Our ISP has warned us that we've donwloaded a 'virus'.

In the lab we download a lot of malware, including the exploits that are often used to install them. We do this using standard consumer ADSL internet connections to reduce the chances of detection by the malware authors and distributors.

Last summer we had just completed a test that involved visiting at least 100 infected websites and allowing them to infect systems. We performed each task at least 12 times, so we potentially downloaded 12,000 threats in one month.

Towards the end of July we received the following (edited) email from our ISP:

Security Notification
---------------------
We have received notification that your IP (xxx.xxx.xxx.xxx) appears to have been compromised.
The IP has likely been infected with a kind of 'virus'  known as a rootkit.
...
Infection: torpig
...

It was interesting to see the attached log file, which recorded the ports and hosts used by the Torpig botnet rootkit (aka Sinowal, Anserin). While I think it's great that some ISPs are taking to trouble to monitor and report malware infections to users, I'm amazed that in the 12 months of using this service (and using it the way that we do!) we've received just one alert.

Related US news: Infosecurity magazine reports that the US Departments of Homeland Security and Commerce is requesting comments on a voluntary programme whereby ISP would notify users of botnet infections.

Saturday, 4 June 2011

Malware runs own DHCP server

Researchers have discovered a variation of the TDSS rootkit that runs its own DHCP server. The upshot is that when computers on the network ask for their IP address and other network configuration details, they are send unhelpful Domain Name Server (DNS) settings.

The DNS settings direct the victims to a malicious webpage and block the rest of the web. The malicious page insists that the user install an application, which will attempt to infect the system. So one infection of TDSS on a network could turn into lots pretty fast.

More details are available at Kaspersky's Securelist.

Wednesday, 27 May 2009

Kaspersky Anti-Virus 2009 (Live CD)

Russian security firm Kaspersky has produced a bootable Linux CD capable of mounting and disinfecting hard disks used by Windows PCs.

The ISO file seems to be freely available, although is tucked away on a part of the company's website that is pretty well hidden. This makes me suspect that it is not intended for general use.

Amed Kamal wrote about it a week ago, providing a direct link.

Using a rescue disc could improve the detection of threats that are usually hard to find and remove, such as rootkits. This is because the Windows operating system is not running - and rootkits hide by tricking the operating system.

UPDATE: There is a newer version available.

Sunday, 23 November 2008

The Complete Internet Security Handbook 2009

If you want to keep your family safe and your data private then The Complete Internet Security Handbook 2009 is the book for you. It includes the following:

What do you want to protect?
Learn how to manage risk and provide the best protection you can for the people and things you care about the most.

Cyber-criminals
Why do viruses, hackers, spam and fake bank websites exist? Discover the criminal underworld of the internet and find out how the scammers and conmen operate.

Chapter 1: Basic Desktop Protection
Take advantage of Windows' built-in security features and protect your computer for free.

Chapter 2: Viruses
Learn how to avoid viruses, recognise them when they appear and remove infections from your computer.

Chapter 3: Hackers, spies and other criminals
Prevent the bad guys on the internet from gaining control of your computer, internet connection and personal details.

Chapter 4: Spam and how to avoid it
Is your email inbox overwhelmed with annoying messages? We'll show you how to regain control and banish spam forever.

Chapter 5: Protect your child
The internet is a great educational resource, but threats abound. Ensure your kids stay safe online with our comprehensive guide.

Chapter 6: Lost and stolen
Reduce the chances of computer theft and encrypt your files to keep them private, even if they are stolen.

Chapter 7: Accidents and malfunctions
Discover the easiest way to keep your files safe and find out how to recover them if the worst happens.

Chapter 8: Personal privacy
Learn how to prevent your personal data falling into the wrong hands.

Chapter 9: Scams, fraud and hoaxes
Learn how to protect yourself against identity theft, email hoaxes and fake websites designed to steal your money.

BONUS CHAPTER: Wireless networking
They are convenient, but how safe are wireless networks? We show you how to build and bullet-proof your network.

The Complete Internet Security Handbook 2009 is available now from Borders and costs £7.99. It will also be available in WHSmiths from 27/11/2008. Amazon is currently selling it for £6.39 (as of 23/11/2008).

ISBN: 1-906372-18-7
Cover price: £7.99
Edited and (mostly) written by Simon Edwards.

Thursday, 2 October 2008

Can rootkits ever be useful?

A security company has developed a tool that aims to protect users from fraud, even if their computers are infected with viruses or other threats. According to Technology Review, Verdasys has developed SiteTrust, which it hopes to license to financial institutions. These in turn would provide software to their customers, who would use it alongside existing security products such as anti-virus and firewalls.

There are two interesting points with Verdasys' approach, as far as I can tell from reading Technology Review's report. The first is the idea that we should assume that everyone's systems are infected with malware. This is a depressing thought, but probably very sensible. The second, and possibly most controversial, is that SiteTrust is "essentially a rootkit."

Verdasys chief technology officer Bill Ledingham reportedly acknowledges the controversy surrounding commercial rootkits, but claims that Verdasys' experience in designing them ensures they won't interfere with a computer's normal use. He also admits that criminals may try to dig even deeper into the system, to undermine SiteTrust, but hopes to stay one step ahead of the hackers.

Remember this: he claims that the rootkit won't interfere with a computer's normal use; and hopes to stay one step ahead of the hackers.

THE PROBLEM WITH ROOTKITS

Rootkits are usually malicious, being designed to allow a program to exert maximum control over a system at a very low level in a secretive way. Online criminals sometimes use rootkits to take control of victims' computer systems, but sometimes a legitimate company chooses to use rootkit-like techniques to protect data in one way or another. This rarely ends well.

Sony has tried this a number of times but, in each known case, experts have noted (or even demonstrated) that an attacker could abuse a system with 'legitimate' rootkit technology installed. This is the main problem with commercial rootkits. They can provide an opportunity for an attacker. When users don't know that the software has been installed, as was the case with Sony's CD copy protection system, there are additional issues of personal privacy.

There may be a further issue of the rootkit interfering with the computer's normal use, but we'd take for granted that a commercial rootkit would not cause obvious problems to the system. Legitimate companies should have better quality assurance than online criminals, after all. So the main issue in this case is whether or not the rootkit could be used as an attack vector. And we won't know that until someone starts to play with the product in a lab.

Every technology company that deals with security hopes to stay ahead of the hackers, but few would claim (behind closed doors) that they are managing to do this. This is why malware exists and why no responsible company would ever claim to offer 100 per cent protection.

While it is possible that a company like Verdasys could produce a successful product that provides no opportunity for an attacker and that always stays one step ahead of the hackers, it is worth remembering that this aim might fail. And what a juicy target SiteTrust would be, if it did. After all, it is a product designed to secure important financial transactions.

Wednesday, 5 September 2007

Sony rootkit (part 2.1)

Sony has agreed to remove the rootkit-like part of its fingerprint scanner/flash drive. An update sometime this month will remove the software's ability to hide directories, a technique that could be abused by an attacker.

Interestingly, Sony has downplayed this episode by claiming that it has not sold many of these secure flash drives, which are no longer being manufactured. It also claims that the fault lies with a Chinese software developer, which wrote the offending code.